
As organizations become increasingly dependent on digital technologies, protecting sensitive information and maintaining secure communication have become essential business priorities. Customers, employees, and business partners expect reliable digital services that safeguard their information and verify identities accurately. Establishing Digital trust requires more than implementing traditional cybersecurity measures. It demands a proactive approach to managing digital identities, certificates, and authentication processes throughout their entire lifecycle. By maintaining control over these elements, organizations can strengthen security, improve operational reliability, and build confidence in every digital interaction.
Understanding the importance of digital trust
Digital trust represents the confidence that individuals and organizations place in digital systems, services, and transactions. It depends on several essential principles, including secure authentication, data integrity, confidentiality, and reliable system performance. When these elements work together, users can interact with digital platforms knowing that their information is appropriately protected.
However, trust can quickly disappear when security incidents or technical failures occur. An expired certificate may interrupt access to an important application, while compromised credentials can expose sensitive business information. These situations demonstrate why organizations must continuously maintain their security infrastructure rather than relying on occasional updates or reactive measures.
The role of digital certificates in secure environments
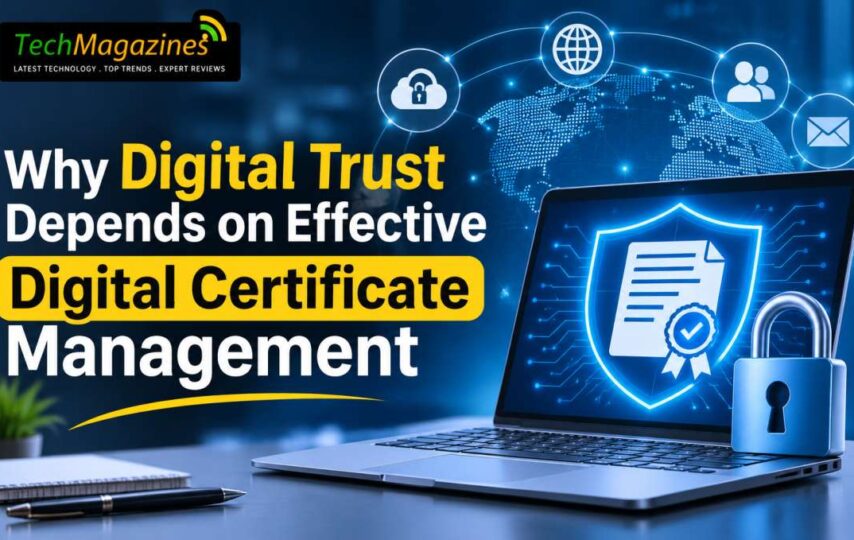
Digital certificates are fundamental components of modern cybersecurity. They establish trusted relationships between users, applications, servers, and connected devices by linking verified identities to cryptographic keys. This enables secure authentication and supports encrypted communication across digital networks.
Organizations use certificates for numerous purposes, including securing websites, authenticating devices, and verifying digital signatures. As businesses adopt additional cloud services and connected technologies, the number of certificates requiring management increases. Consequently, maintaining accurate oversight becomes essential for preventing security vulnerabilities and ensuring uninterrupted digital operations.
Why poor certificate management creates risks
Managing digital certificates becomes increasingly challenging as organizations expand. Certificates have different expiration dates, configurations, and operational requirements. Without centralized oversight, IT departments may struggle to identify where certificates are installed or when they require renewal.
Unexpected expiration can interrupt websites, applications, and authentication services, potentially affecting employees and customers. Poorly configured certificates may also weaken security controls. These risks highlight the importance of establishing structured management procedures that provide continuous visibility and allow organizations to identify potential problems before they affect critical systems.
How effective certificate management strengthens trust
Implementing reliable Digital certificate management allows organizations to maintain control over certificates throughout their operational lifecycle. Centralized management provides visibility into certificate inventories, validity periods, deployment locations, and security configurations. This makes it easier to identify potential vulnerabilities and maintain consistent protection across different environments.
Automation further strengthens these capabilities by reducing reliance on manual processes. Certificates can be monitored continuously, renewal procedures can be initiated before expiration, and compromised credentials can be revoked when necessary. By preventing avoidable disruptions and maintaining secure authentication, organizations create more dependable digital services that support lasting confidence among users and business partners.
Supporting compliance and accountability
Regulatory requirements increasingly emphasize the importance of protecting sensitive information and maintaining secure digital identities. Organizations operating within regulated industries must demonstrate that appropriate security measures are implemented and consistently maintained.
Effective certificate management supports these responsibilities by improving traceability and providing reliable records of certificate activities. Security teams can document issuance, renewal, and revocation procedures while monitoring compliance with internal policies. This structured approach simplifies audits and helps organizations demonstrate accountability without creating unnecessary administrative complexity.
Improving operational efficiency through automation
Beyond strengthening security, certificate management can significantly improve operational efficiency. Manually tracking certificates across numerous systems requires considerable time and increases the possibility of human error. As certificate volumes grow, these administrative responsibilities can become difficult to manage effectively.
Automated management solutions help reduce repetitive tasks and allow IT teams to focus on strategic security initiatives. Monitoring, notifications, and standardized renewal processes minimize unnecessary interruptions while supporting consistent operations. As a result, organizations can maintain reliable digital services without continuously increasing the resources dedicated to routine certificate